Cristian Farias

Full-Stack Developer

I design, build and deploy complete web applications, from the interface to the backend, with a focus on performance and security. I work with React, Next.js, TypeScript, Java, Spring Boot, Node.js and PostgreSQL. I built a Kafka-based reservation system deployed on AWS and carried out a web security audit following the PTES methodology.

Cristian Farias face in a circular shape

Selected

Projects

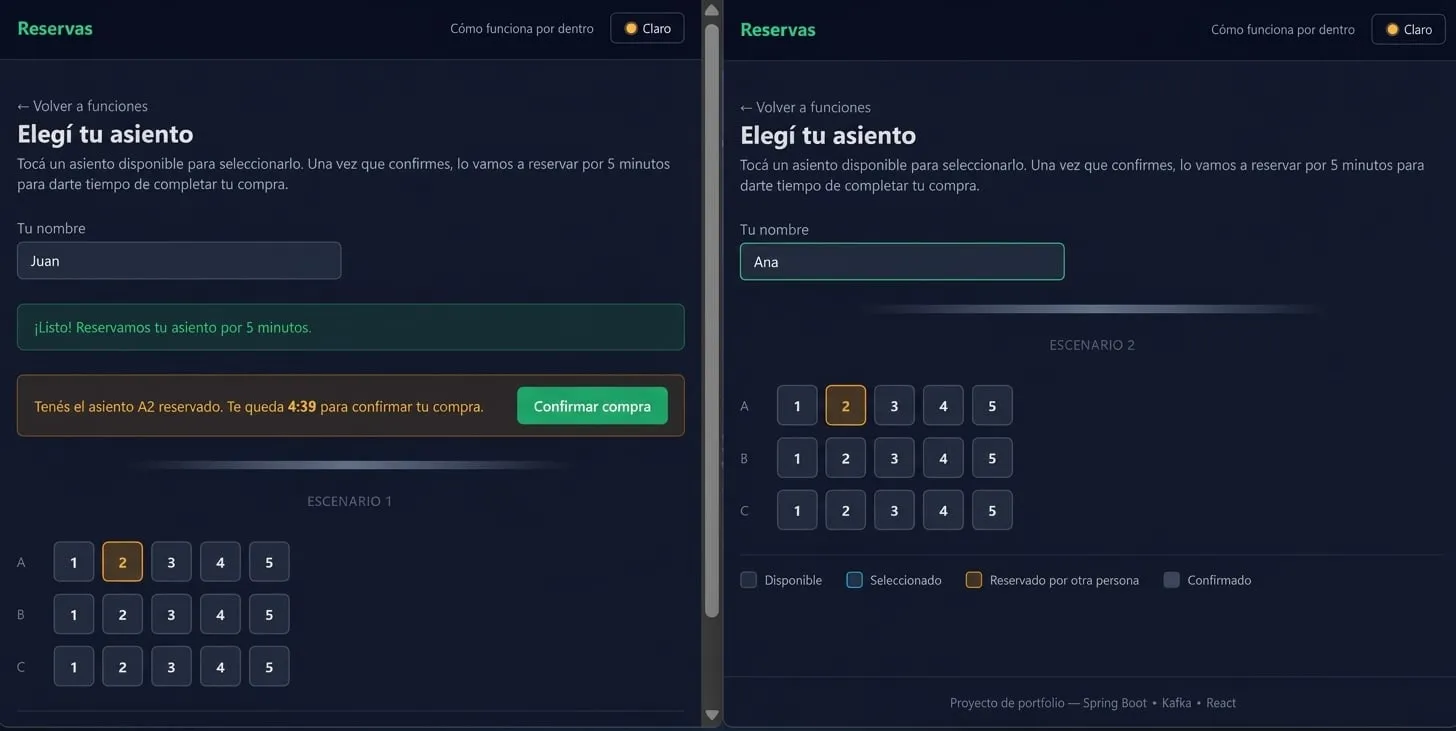
Seat reservation system with Kafka - application screenshot

Seat reservation system with Kafka• Personal project

  • Designed event-based concurrency control: when several requests target the same seat at once, only one succeeds.
  • Implemented live updates over WebSocket and 11 integration tests with Testcontainers.
  • Deployed on AWS EC2 with Docker.
Java 21
Spring Boot
Kafka
PostgreSQL
React
Docker
AWS EC2
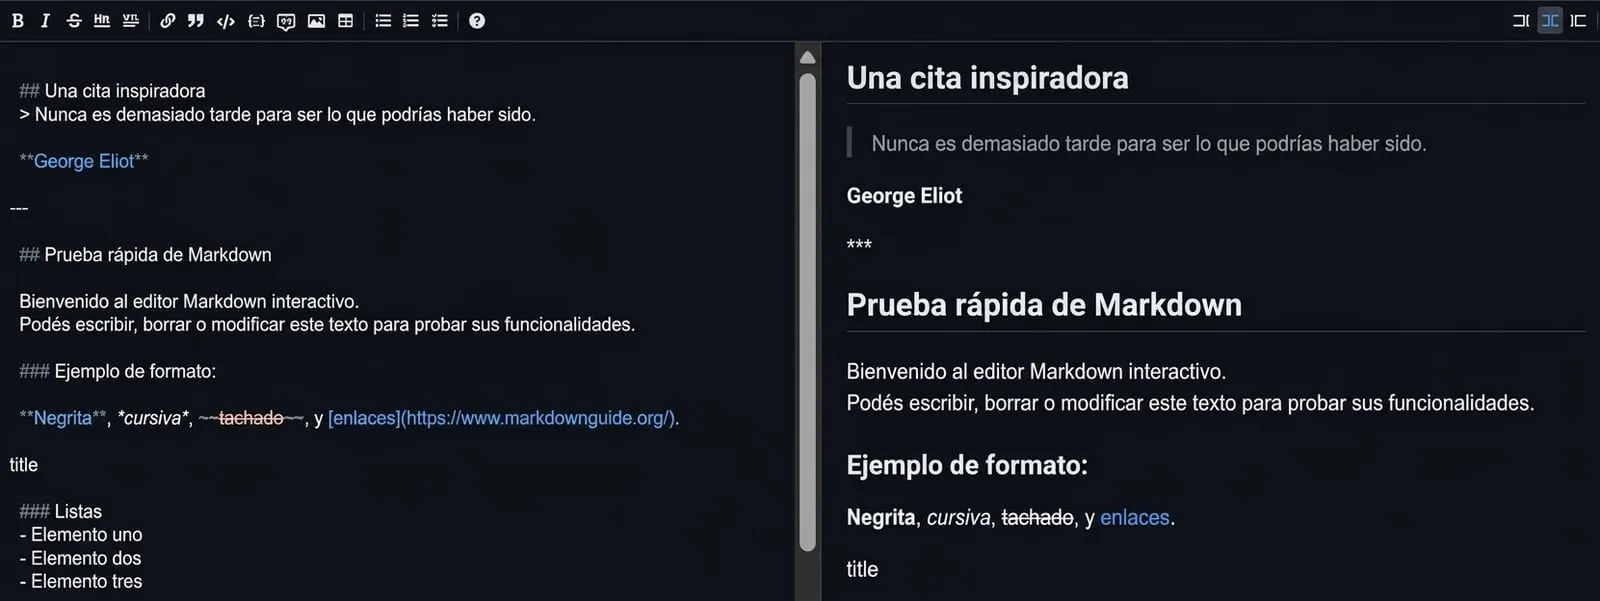
Markdown Editor Online - application screenshot

Markdown Editor Online• Personal project

  • Editor with real-time preview, running entirely in the browser.
  • Deployed on Vercel, with the source code available on GitHub.
Next.js
React
Tailwind CSS
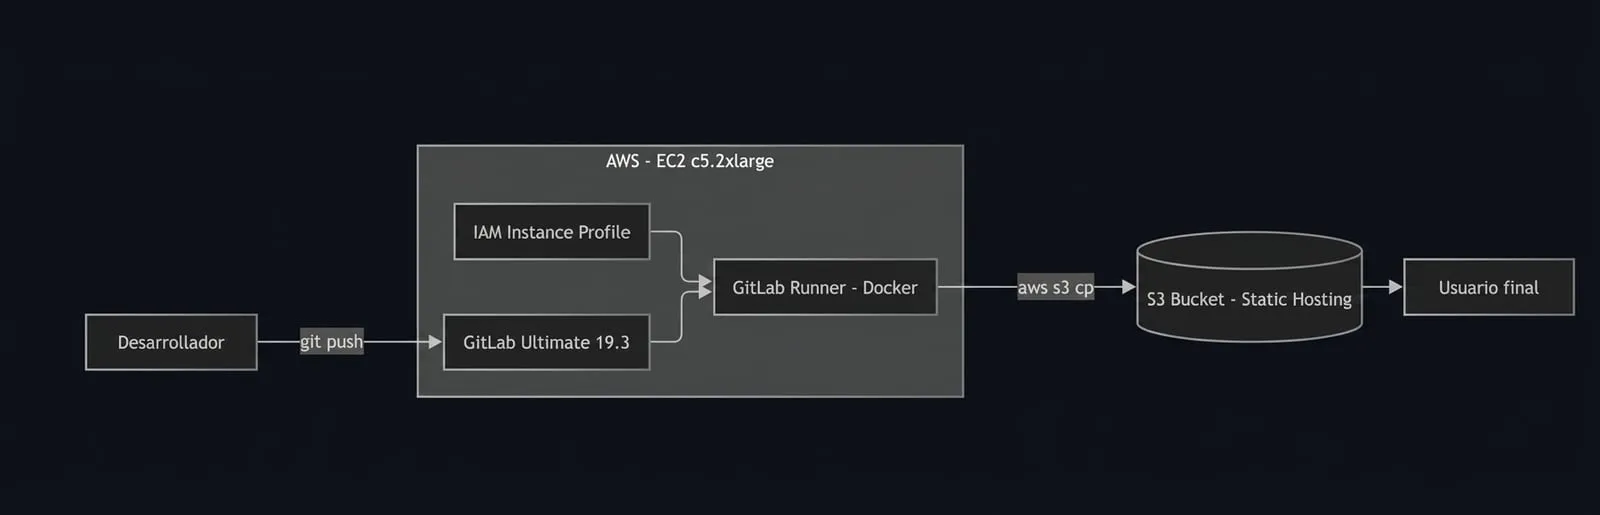
GitLab CI/CD pipeline on AWS - pipeline screenshot

CI/CD pipeline on AWS• AWS Workshop lab

  • Documented and reproduced a GitLab CI/CD pipeline (build, test and deploy to S3) with a Runner on EC2 and an IAM Instance Profile.
  • Diagnosed and fixed three chained failures in the original workshop.
GitLab CI
AWS EC2
S3
IAM
Docker

Case study

Web security audit

Black-box penetration test on the web infrastructure of a public institution, with a formal contract and authorization, following the PTES methodology.

  • 6Critical
  • 9High
  • 4Medium
  • 6Informational

25 findings, scored with CVSS v3.1

Types of findings

  • Unsupported component with a remote code execution vulnerability (verified by version, not exploited).
  • Personal data exposed without authentication.
  • Outdated remote access service with password authentication enabled.
  • CSRF token present in the form but never validated on the server.
  • No account lockout or rate limiting.
  • User enumeration through a public API.
The application code was reasonably well configured, but the underlying infrastructure had accumulated critical technical debt. Administrator passwords withstood brute force, and there was no exploitable SQL injection or XSS.

Deliverables: report with evidence, CVSS v3.1 scoring, an end-to-end attack chain and remediations per platform.

Kali Linux
Nmap
Burp Suite
Metasploit
sqlmap
Hydra

Information anonymized for confidentiality.

My

Stack

React logo
Next.js logo
TypeScript logo
Tailwind CSS logo
Java logo
Spring Boot logo
Node.js logo
PostgreSQL logo
Apache Kafka logo
Docker logo
AWS logo
React logo

JavaScript library for building UIs

React

Library for building interfaces from reusable components. It is the foundation of my frontends.

Training and

Credentials